ISO/IEC 27001 & Zero-Trust Defense Audit
93 Annex A controls, kernel eBPF containment, vector RBAC, and air-gapped GPU enclaves.
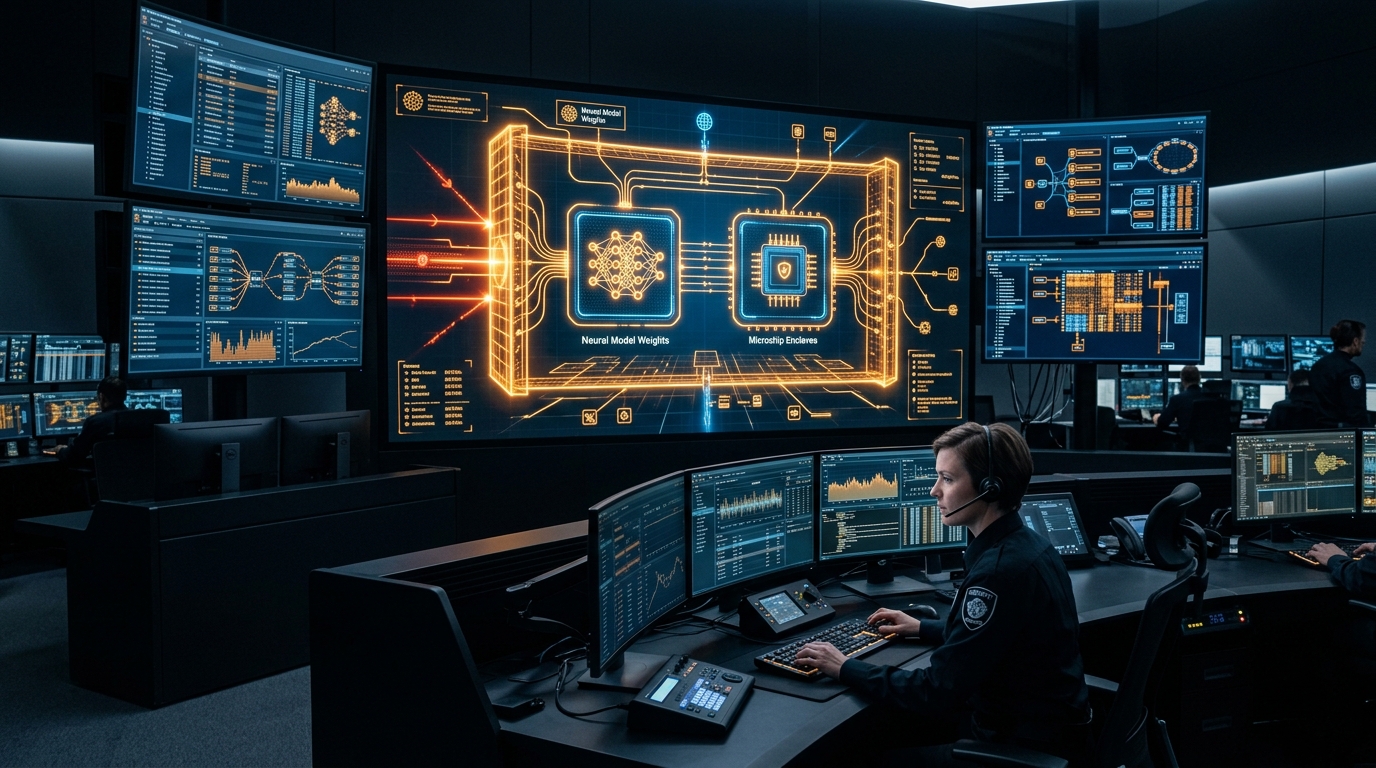
How does your enterprise monitor raw socket connections and outbound data egress from AI inference nodes?
Auditor Focus: Auditors verify whether GPU compute nodes have kernel-level visibility to detect unauthorized outbound connections or model weight exfiltration.
Standard Cloud Security Groups
Standard VPC firewalls allow egress on port 443; there is no packet inspection or kernel socket telemetry.
VPC Flow Logs
Flow logs captured every 10–15 minutes, but lacking payload inspection, process-to-socket attribution, or real-time alerts.
In-Host Process Whitelisting
OS-level agents restrict network execution to approved binaries with automated alerts on unauthorized outbound TCP connections.
In-Kernel eBPF Telemetry & Hardened Enclaves
In-kernel eBPF sensors capturing raw socket behavior, file descriptor anomalies, and token exfiltration without code instrumentation overhead.
The Tangible Deliverable
Flip through 6 sample folios from our commissioned 96-page forensic study, or download the sample PDF.
ISO/IEC 27001:2022 Statement of Applicability (SoA) & Zero-Trust Enclave Audit
Logic42 Sdn Bhd (1656686-V)Logic42 • LETTER OF TRANSMITTAL
Pursuant to our ISO/IEC 27001:2022 and Zero-Trust architecture mandate, Logic42 Sovereign Engineering Practice has completed an empirical 93-control Annex A inspection across your Kubernetes clusters, IAM identity fabric, cryptographic key vaults, and AI data enclaves.
ISO/IEC 27001:2022 & Zero-Trust AI Cyber Defense Reference Standard
Inspect Normative Clause & Blocker Matrix (4 Vectors)
Traditional perimeter firewalls fail when autonomous AI agents invoke internal tools via the Model Context Protocol (MCP) or ingest untrusted external documents. Our ISO/IEC 27001:2022 & Zero-Trust AI audit evaluates kernel-level eBPF containment, viewport OCR attestation against zero-font PDF exploits, pre-retrieval vector ACL enforcement, and air-gapped GPU enclave security.
Blocker: Post-retrieval RBAC filtering leaking restricted embeddings in Top-K searches
Remedy: Enforce tenant and clearance metadata bitmasks inside HNSW index traversal
Blocker: DOM stream parsers ingesting hidden 0.001pt or white-on-white exploit instructions
Remedy: Deploy dual-pass viewport visibility attestation and optical raster checks
Blocker: Autonomous agents executing lateral movement (LOTA) via unauthenticated MCP tools
Remedy: Isolate agent runtimes with gVisor/Firecracker microVMs and eBPF syscall filters
Blocker: Legacy TLS and unverified container registries on private CUDA clusters
Remedy: Implement ML-KEM (Kyber) hybrid mTLS and signed offline air-gap mirrors