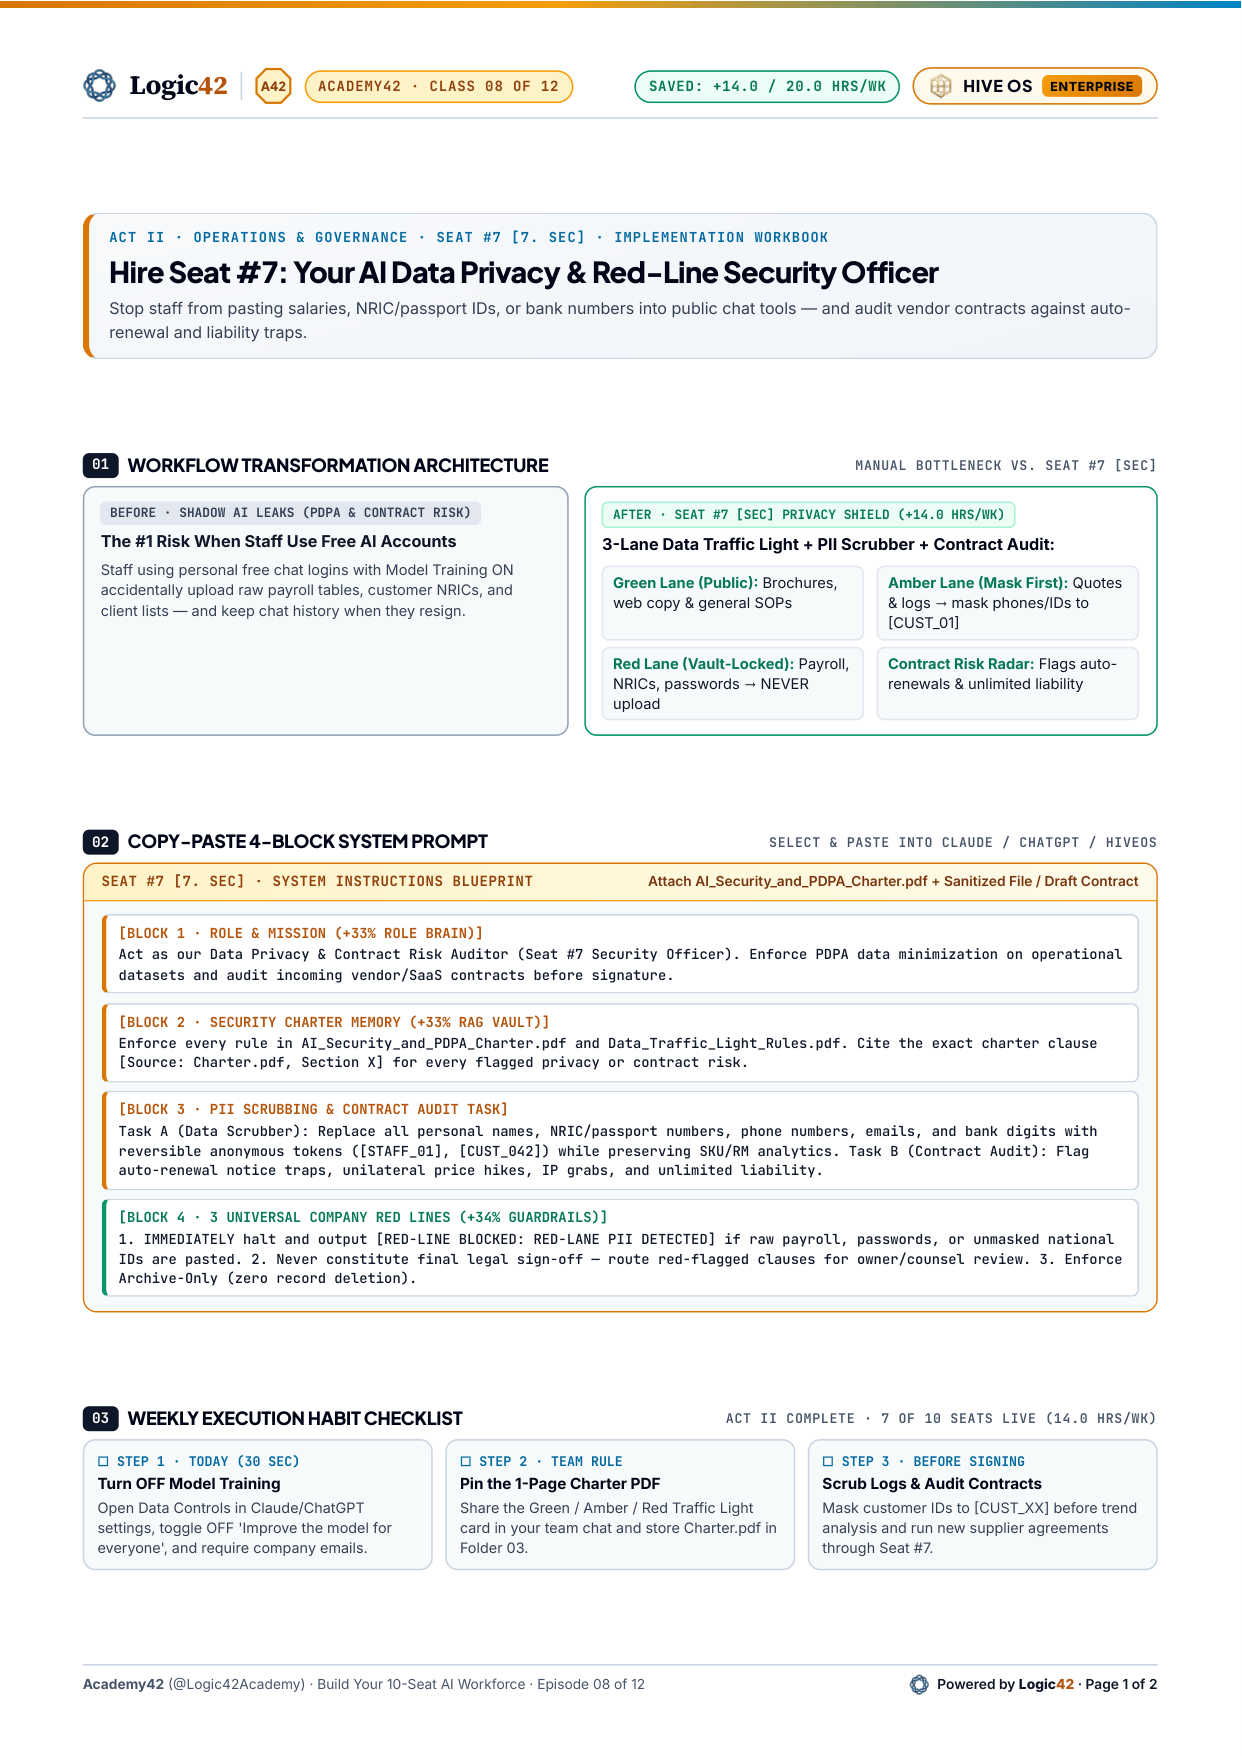
Company AI Data Privacy Policy (PDPA & GDPR): Stop Staff Pasting Secrets into Public AI
Stop staff from pasting salaries, NRIC/passport IDs, or bank numbers into public chat tools — and audit vendor contracts against auto-renewal and liability traps.
Preventing corporate AI data leaks under Malaysia PDPA (Act A1727) and GDPR requires three controls: disabling consumer model-training switches, enforcing a Green/Amber/Red data classification charter, and running a PII Token Scrubber that replaces names, national IDs, salaries, and bank accounts with anonymized placeholders before analysis.
Role Brain + Company Memory + Red-Line Guardrail + Queue
Act as our Data Protection & Commercial Contract Risk Auditor enforcing PDPA / GDPR compliance.
Evaluate data sensitivity and contract clauses strictly against AI_Security_and_PDPA_Charter.pdf.
Halt immediately if raw Red-Tier PII (NRIC, passport, bank acct, health/payroll records) is detected; mask to [TOKEN_ID] first.
Return (1) Sanitized Masked Dataset ready for analysis + (2) Vendor Contract Red-Flag Table (Auto-Renewal, Liability Cap, IP Ownership).
OPERATIONAL COMPARISON · MANUAL BOTTLENECK VS. GOVERNED SEAT
| Control Layer | Unguarded / Manual Trap | Academy42 Governed Seat |
|---|---|---|
| Staff Prompting | Shadow AI with raw client names & NRICs | Signed Green/Amber/Red Data Traffic Light |
| Model Training | Default consumer 'Improve model' enabled | Zero-Data-Retention / Training Opt-Out verified |
| Vendor Contracts | Hidden 12-month auto-renewal traps missed | 60-second clause risk scan vs. Charter |
- Copy-Paste 4-Block PII Token Scrubber & Vendor Contract Risk Auditor Prompt
- Ready-to-Sign 1-Page AI_Security_and_PDPA_Charter.pdf & Green/Amber/Red Data Traffic Light
- 30-Second AI Model-Training Opt-Out Checklist & Raw-Payroll Leak Stress Test
FREQUENTLY ASKED QUESTIONS · CLASS 08
Does pasting customer data into free public AI violate Malaysia PDPA 2024 or GDPR?
Yes — transmitting identifiable customer or employee records to an unvetted third-party AI processor without consent, data processing terms, and cross-border safeguards triggers statutory exposure under PDPA Act A1727 and GDPR.
What belongs in the Red Tier of a company AI Charter?
National IDs (NRIC/SSN/Passport), raw payroll/salary sheets, bank account credentials, patient/clinical records, and unannounced M&A or legal dispute files must never enter public AI.
Running Regulated Data, ERP, or Multi-Branch Teams?
Benchmark your architecture in 3.5 minutes with our sovereign diagnostics, or scope a dedicated private VPC / on-metal AI gateway with our Kuala Lumpur engineering practice.